

01
Which tools can we use?
A company subscription, a personal account or AI built into an app? Establish a shared view of approved tools.
Your team is already using AI. Give them clear rules to work with.
We assess the tools, set the rules and prepare your people. From the first question to everyday practice.
AI, data protection and information security, together.A summary, a customer email or an automated workflow involves tools, data and responsibilities. We help you make sense of them.
A company subscription, a personal account or AI built into an app? Establish a shared view of approved tools.
Customer data, internal documents, business information. We review data processing for the specific tool and use case.
Make it clear who approves new uses, who checks the output and where staff can turn for help.
ChatGPT, Copilot, Gemini, Claude, browser extensions and AI agents: we start with how your people actually work.
Five connected areas, tailored to your tools, data and workflows.
After the assessment, we agree the work, documents and training you need, then provide a tailored proposal.
Based on the information available, we assess the AI tools, company subscriptions and integrations in use.
An AI inventory and an approved tool list tailored to your organisation.
We create clear internal rules for introducing new tools and using them day to day.
A practical policy with clearly assigned responsibilities.
We tailor personal data handling and its documentation to the specific AI use case.
New or updated documents needed for the specific data processing.
We assess whether a data protection impact assessment (DPIA) is needed. If it is, we identify risks and measures to reduce them.
A documented assessment of the need for a DPIA, followed by a DPIA where warranted.
We translate the rules into guidance for people’s roles and the tools they actually use.
Role-specific learning materials and staff prepared to use AI.
Dr Szabolcs Gyurkovics delivers the AI service, backed by zemITis expertise in data protection and information security.
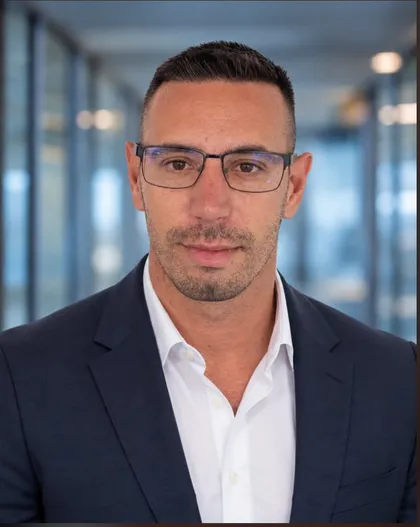
Lawyer and cybersecurity law specialist. More than eight years of data protection experience, supporting AI and digitalisation projects.
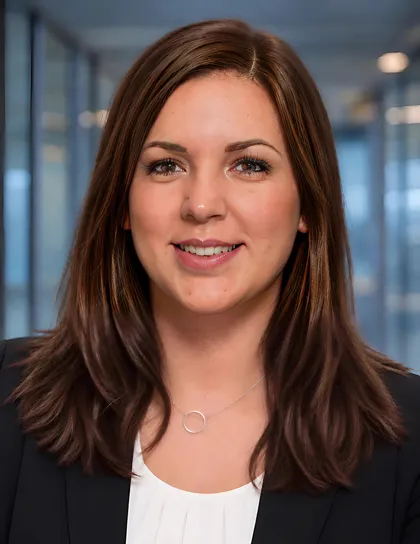
Lawyer and cybersecurity legal specialist with five years at Hungary’s data protection authority. Data processing, privacy notices, impact assessments and staff training.
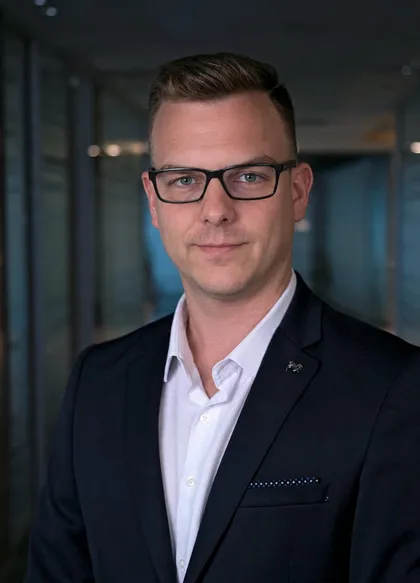
CISA, CISM and ISO/IEC 27001 Lead Auditor. More than ten years of experience in IT compliance, audit and risk management.
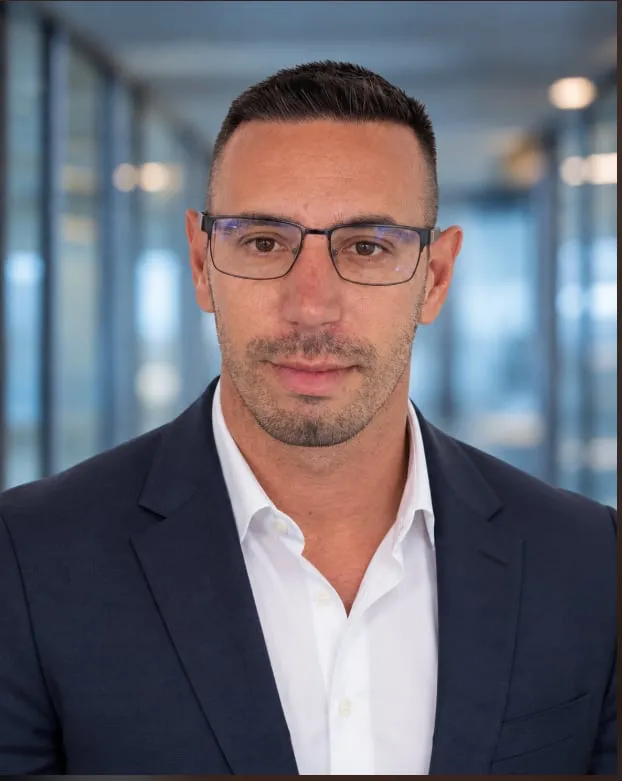
Lawyer and cybersecurity law specialist; data protection and AI compliance expert
LinkedIn profileSzabolcs has more than eight years of experience in data protection, in both corporate and regulatory settings. He earned his law degree at the University of Pécs, followed by a postgraduate qualification in cybersecurity law at Széchenyi István University. He has worked as a data protection expert at Takarékbank, Hungary’s National Authority for Data Protection and Freedom of Information (NAIH), and Szerencsejáték Zrt.
In recent years, he has focused on data protection support for IT, digitalisation and AI development projects. His work has included handling personal data breaches, preparing privacy notices and cookie policies, and carrying out legitimate interest assessments.
He has also developed an AI solution for data protection professionals. He regularly contributes to Jogi Fórum, writing about data protection compliance in modern technologies.
We help establish regulatory and data protection frameworks for existing and planned AI use.
We discuss your goals, tools and existing rules, then agree the scope of the assessment.
Based on the findings, we prepare your tool list, usage policy and the data protection documents you need.
We walk you through the materials, prepare your staff and agree the next steps for the people responsible.
AI is already part of your work.
Make safety part of it, too.
Let’s start with the tools your team uses and where clearer rules would help.